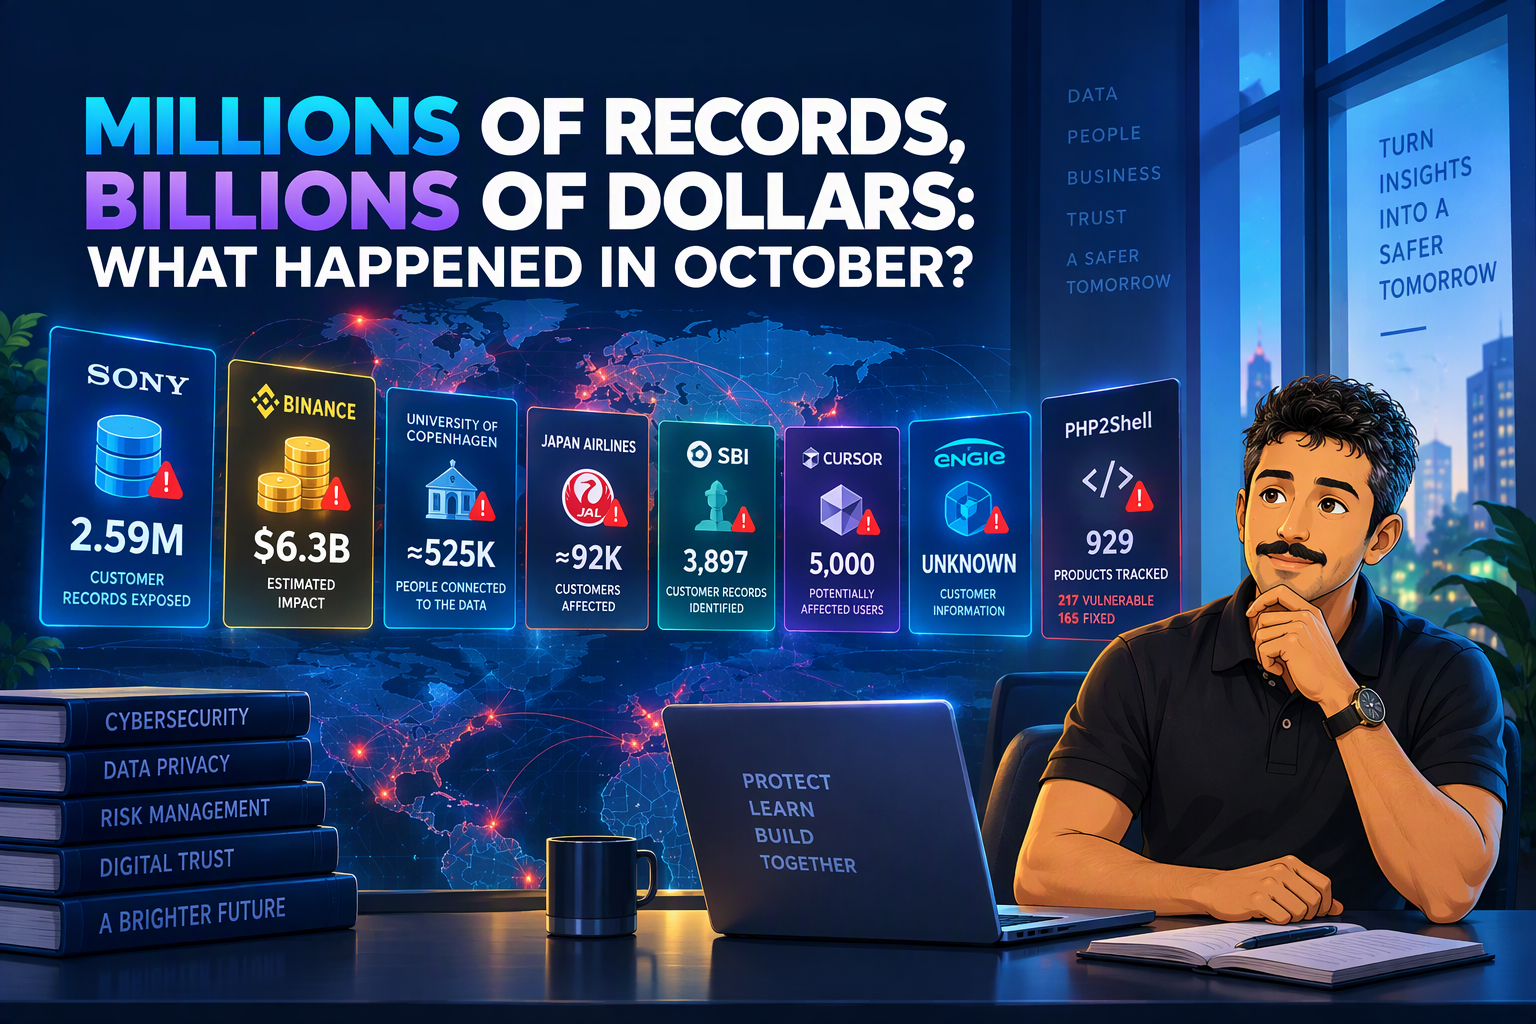
October was a rough month for cybersecurity. Sony reported millions of customer records exposed, Binance made headlines over billions of dollars, customer information connected to a major bank appeared on the dark web, and a malicious extension reached developers through a marketplace they trusted.
These stories look very different, but they raise the same question: what happens when we put the numbers next to each other?
The largest number does not always describe the largest impact. First, we need to understand what it measures.
The month in a few numbers
Sony Network Communications reported 2,585,481 exposed customer records connected to its So-net and related services. The University of Copenhagen disclosed an incident involving data connected to around 525,000 people, while Japan Airlines reported approximately 92,000 affected customers through its reservation technology provider, Amadeus.
In banking, State Bank of India identified 3,897 customer records containing personal information during a preliminary review of about 375,000 records found on the dark web. The bank said the source and full extent of the exposure were still being investigated.
2.59M
Sony So-net
Customer records exposed
≈525K
Copenhagen
People connected to the data
≈92K
Japan Airlines
Customers affected
3,897
SBI
Customer records identified
At first glance, this looks like an easy ranking. Sony clearly has the longest bar. But there is already a problem: one organisation counted records, another referred to people, and another counted customers.
Published affected populations
How the selected disclosures compare
The figures use the terminology published by each organisation. Records, people and customers are similar indicators of scale, but they are not identical units.
Then there is Binance
Binance does not fit into that chart. Its October incident was reported through a completely different measure: money. Contemporary reporting placed the estimated impact at approximately US$6.3 billion, with about US$3 billion located at that stage.
Binance: reported financial impact
Putting US$6.3 billion beside 2.59 million customer records would make a dramatic graphic, but it would be a poor comparison. One number measures financial value. The other measures data exposure.
Some numbers need an asterisk
Cursor disclosed another type of incident on October 29. Modified versions of a Claude Code extension were available through its extension marketplace for roughly 11 hours. Cursor said the code collected device information and attempted to create persistent access through SSH.
Reporting placed the maximum potentially affected population at 5,000 users. That wording matters. “Up to 5,000” is not the same as confirming that 5,000 machines were successfully accessed.
ENGIE presents the opposite problem. The company confirmed that French customer information had been taken through a marketing platform used by business partners, but the affected population was not publicly quantified. That value should remain unknown. Unknown does not mean zero, and it should not become an invented estimate just to fill a chart.
A small but important distinction
Confirmed, estimated, maximum possible and under investigation are not interchangeable labels.
And sometimes there is no victim count
PHP2Shell was one of October’s largest technical concerns, but it cannot be measured using exposed records or stolen money. The two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, could allow attackers to run code remotely on vulnerable systems without first signing in.
By October 30, an operational tracker covered 929 products, including 217 listed as vulnerable and 165 listed as fixed. Here, the useful numbers describe software exposure and patching progress, not confirmed victims.
PHP2Shell tracker
Product status reported on October 30
So, which incident was the biggest?
There is no honest single answer. Sony produced the largest comparable record count in this selection. Binance carried the largest reported financial figure. Cursor showed how a trusted software channel could reach developer machines. PHP2Shell was better understood through vulnerable products and patching progress.
October’s incidents also show how often the company in the headline is not the only organisation involved. Japan Airlines was affected through Amadeus. ENGIE reported exposure through a partner’s marketing platform. Cursor’s incident involved its extension marketplace. The path followed by the data matters as much as its final destination.
For the rest of us, the practical advice remains familiar for a reason: use different passwords for important accounts, enable multi-factor authentication and be careful with unexpected messages after a breach becomes public. Real personal details can make a fake banking call or phishing email sound convincing.
What the numbers really say
Before reacting to a large number, check its unit, definition and source. Records, people, money, vulnerable products and estimates tell different parts of the story.
This article covers selected major incidents disclosed during October 2026. It is not a complete list of every cyber incident reported during the month.
